How RoninArmor Compares to
Legacy Security Suites.
Many commercial server security tools in use today were designed over a decade ago. They rely on heavy scripting interpreters, unoptimized virus definition loaders, and constant hard drive reading that causes high disk latency and slows down client websites.
RoninArmor was engineered from the ground up as a native compiled defense engine. Here is a factual, side-by-side comparison of features, performance, and overall costs.

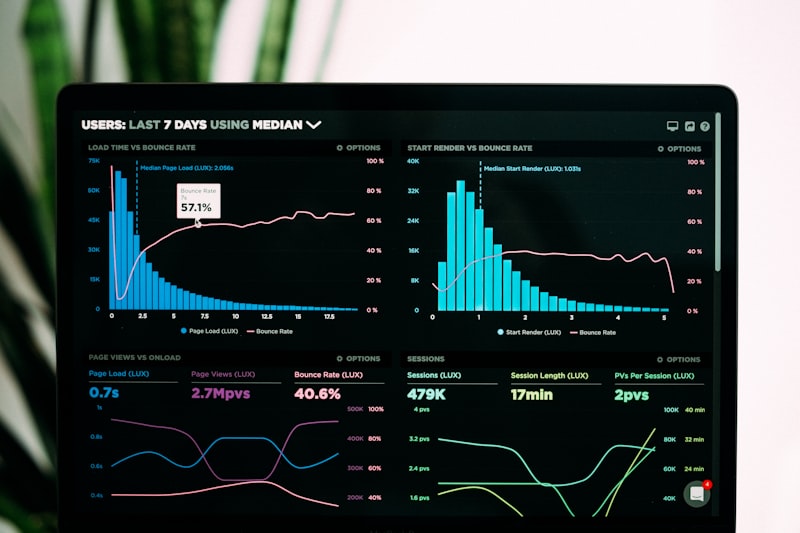
Real Server Performance Impact
Security should never slow down genuine website visitors or degrade search rankings. We measured identical hosting environments running legacy tools versus RoninArmor.
Time to First Byte (TTFB)
Delay added to incoming visitor web requests before reaching application website code.
CPU Load During Active Scans
Processor thread saturation measured while actively scanning 50,000 customer files.
Background Memory Footprint
Permanent system memory consumed by background security daemons during normal operation.
Complete Technical Comparison Matrix
A structured, side-by-side technical evaluation across all server security layers.
| Capability & Architectural Standard |
ClamAV + CSF
free / manual setup
|
Legacy Suites
commercial tiered
|
Recommended
RoninArmor
|
|---|---|---|---|
| 1. Core Architecture & System Performance | |||
| Software Execution Engine How security daemons execute and communicate on host systems. | Perl Scripts / C | Interpreted Scripts Hybrid | Native Compiled Daemon |
| Firewall Event Logging (Disk Wear) Impact of high-frequency firewall logs on physical SSD storage drives. | Physical Disk Text Logs | Heavy SSD Writing (I/O Wait) | Fast Memory (/dev/shm) |
| Database Concurrency & Pooling Prevents locked database crashes during high-traffic flood attacks. | Single Database Lockups | Multi-Pool WAL Engine | |
| 2. Filesystem & Malware Defense | |||
| Real-Time On-Access File Inspection Intercepts malware uploads the exact millisecond they hit user folders. | Cronjob Only (Delayed) | ||
| Instant Immunity Mode (chmod 0000) Strips execution rights immediately without breaking website features. | Quarantine Move Only | ||
| SEO Spam, Gambling & Phishing Filter Detects injected betting keywords, adult redirects, and phishing pages. | Partial Regex Rules | ||
| 3. Web Application & Network Firewall | |||
| Web Application Firewall (WAF) Filters SQL Injection, XSS, RCE, and automated scanning probes. | |||
| Zero-Day Virtual Patching Shields WordPress, WooCommerce, and Joomla before patches release. | |||
| Aegis Network Firewall & LFD Auto-bans brute-force attempts on SSH, FTP, cPanel, DirectAdmin, Webmail. | |||
| Capman Captcha & Virtual Waiting Room Absorbs Layer 7 flood surges and challenges bots without extra CDNs. | External Cloudflare Only | ||
| NetGuard Network Telemetry & Sniffing Live interface monitoring for bandwidth and connection flood limits per IP. | |||
| 4. Application Runtime & Advanced Engines | |||
| PHP Runtime Protection (RASP) Terminates unauthorized shell execution and eval commands in memory. | PHP 5.6 to 8.5 Hook | ||
| MailGuard Outbound Spam Throttling Stops compromised accounts from blacklisting the mail IP on Exim/Postfix. | SpamAssassin Only | Extra License Required | |
| Multi-Provider EasySSL Automation Automatic failover between Let's Encrypt, ZeroSSL, and Google Trust. | Single Authority Only | Multi-CA Fallback | |
| Account Resource Governor Limits CPU and memory per user without needing CloudLinux OS. | Requires CloudLinux ($18+/mo) | ||
| AuthGuard Root 2FA (SSH & Console) Enforces two-factor verification on direct root terminal logins and sudo. | Telegram, App, Passkeys | ||
| Database Threat Scanner (DB-Scan) Scans database tables for injected rogue administrators and scripts. | |||
| 5. Pricing Structure & Scalability | |||
| Billing Model How you are charged as you host more websites on the server. | Free (Self-Managed) | Tiered Per-User Penalty Fee | Flat Per-Server Price |
| Account & Domain Restrictions | Unlimited (No Support) | Capped (30, 250, etc.) | Unlimited Domains |
Total Cost of Ownership (TCO)
Legacy security providers penalize your growth. As you add more hosting accounts or domains to your server, your security bill skyrockets automatically. RoninArmor uses a strictly flat, per-server pricing model.
Stop Paying Penalties for Growing Your Business
If you run a web hosting company or manage client sites, hosting more users on a powerful dedicated server is how you maintain profitability. Your security software should not take a percentage of that profit with tiered account fees.
- Zero limits on cPanel, Plesk, or DirectAdmin accounts
- Zero fees for parked, addon, or staging domains
- 100% predictable monthly operating costs
Monthly Cost vs Number of Accounts
Comparing costs as you grow from 10 to 250 accounts on one server.
Built for Developers, Agencies & Hosters
Designed for clean server automation with zero interactive configuration prompts.
Ansible & Cloud-Init Ready
Our one-line installation command runs silently. Integrate it directly into automated server setup scripts without manual intervention.
Billing & API Integration
Automate license provisioning and client management with our REST API, designed to integrate with custom hosting and billing portals.
Clean Server Removal
We respect your server operating system. If you ever uninstall, our removal routine restores original configurations cleanly without leaving orphaned files.
Technical Clarifications
Common questions regarding compatibility, migrations, and migration from legacy tools.
Will RoninArmor conflict with other commercial security tools?
Do I need to install a special operating system to limit user CPU and memory?
How does memory-based logging protect physical server storage drives?
/dev/shm), rotating and managing data in memory so your physical drives stay fast and responsive.
Upgrade Your Server Infrastructure.
Replace legacy tools with an efficient, all-in-one defense suite. Create an account to deploy your server licenses in minutes.